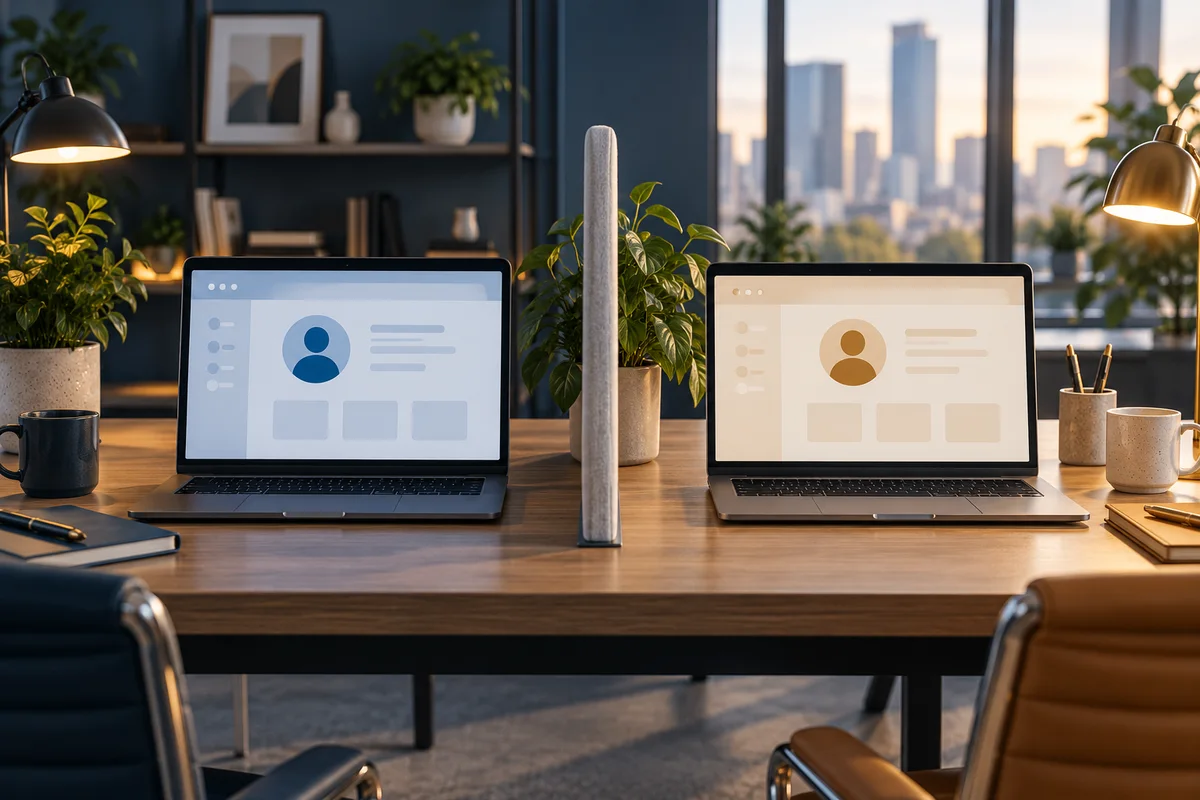
The avatar at the top of a browser and the avatar inside a website can represent different accounts. That distinction matters when one person supports several organizations or uses both work and personal services on one computer. A colorful profile label can make a window recognizable without proving which organization a website will open.
This checklist addresses account context during everyday browser work. It does not replace account provisioning, employee offboarding or an organization's access rules. Use it within the business browser readiness plan whenever an otherwise working application opens in the wrong workspace.
Separate the three identity questions
First identify the operating-system session. Next identify the browser profile. Finally identify the account and organization shown inside the business website. Record the approved identifiers that help support staff distinguish them, not credentials or authentication codes.
Chrome profiles keep browser information such as bookmarks and history separate. Google also warns that someone with access to the device can switch to another Chrome profile. Profiles therefore help organize work but must not be presented as isolation from another person using the same unlocked computer.
Before you open sensitive work
- Is this the person's authorized workstation session?
- Is the intended browser profile selected?
- Does the website display the correct account and organization?
- Is the user authorized for the action they are about to perform?
If the third answer is unclear, stop at the account chooser or ask the application's administrator. Do not infer access from a familiar logo, a saved bookmark or a page that happens to load.
Choose a harmless identity test
Use a sample record or an organization-specific landing page that does not expose private information. The expected result should be recognizable without opening another person's mailbox or customer file. A profile named “Office” is not enough; document the website's own account indicator and where the user can check it.
Test one normal route at a time. Start from the approved bookmark, then repeat from a representative email link or desktop shortcut. If the second route opens a different browser, use the link-routing guide before changing the profile setup. This prevents an entry-route problem from becoming a confusing sequence of repeated account changes.
Decide what belongs in the profile
Ask the support owner which browser information may be synchronized and where. Do not automatically sign a business browser into a personal account merely to recover familiar bookmarks. Google's Workspace browser setup guidance describes account and browser setup options; the organization's approved configuration still determines which options are appropriate.
Keep the handoff narrow. A bookmark list may be useful, while copying saved passwords or an entire profile directory can introduce unnecessary exposure and confusion. If migration is needed, define the approved information, account and destination first. A successful import does not establish that every saved session or application permission moved correctly.
Downloads deserve their own check. Switching profiles should not be assumed to provide a separate approved business filing system. Follow a dummy report into its actual location using the file-handoff checklist, and confirm the destination fits the organization's information-handling practice.
Resolve mismatches without erasing the evidence
Record which route produced the unexpected account, the visible organization name and the affected application. Redact sensitive information from screenshots. Do not delete profiles as a first diagnostic step: Google's profile documentation states that removing a profile erases its local browser information.
If a new authorized profile is proposed, decide what must be preserved before making it. Keep any old profile retirement separate from the diagnosis, with an owner-approved data decision. Likewise, do not clear all browser data merely because one site selected the wrong account. Capture the specific behavior and let support choose a proportionate fix.
Verify the next working session
Close the browser after saving work, reopen it through the normal shortcut and repeat the harmless identity test. Check any site permissions needed for the task without granting unrelated access. A configuration that only works while the technician's window remains open is not a complete handoff.
For ongoing workstation support, discuss the account-context problem through managed IT services. Describe the route and the mismatch rather than sending a password or an exported session. That gives the technician useful evidence while keeping authorization decisions visible.
Reviewed October 24, 2026. Browser controls and supported features vary by version and organizational policy. The test procedures are proposed office checks, not vendor certification.